Network Security
Layered Security on an SMB Budget: How GFI Tools Work Together
Build real cybersecurity protection without enterprise costs. Here's how GFI's tools combine to protect T&T businesses.
August 16, 2026
5 min read
Insights, tutorials, and news from our IT experts in Trinidad & Tobago.
Build real cybersecurity protection without enterprise costs. Here's how GFI's tools combine to protect T&T businesses.
Stop guessing about patches. GFI LanGuard scans, reports, and deploys updates across your entire network from one console.
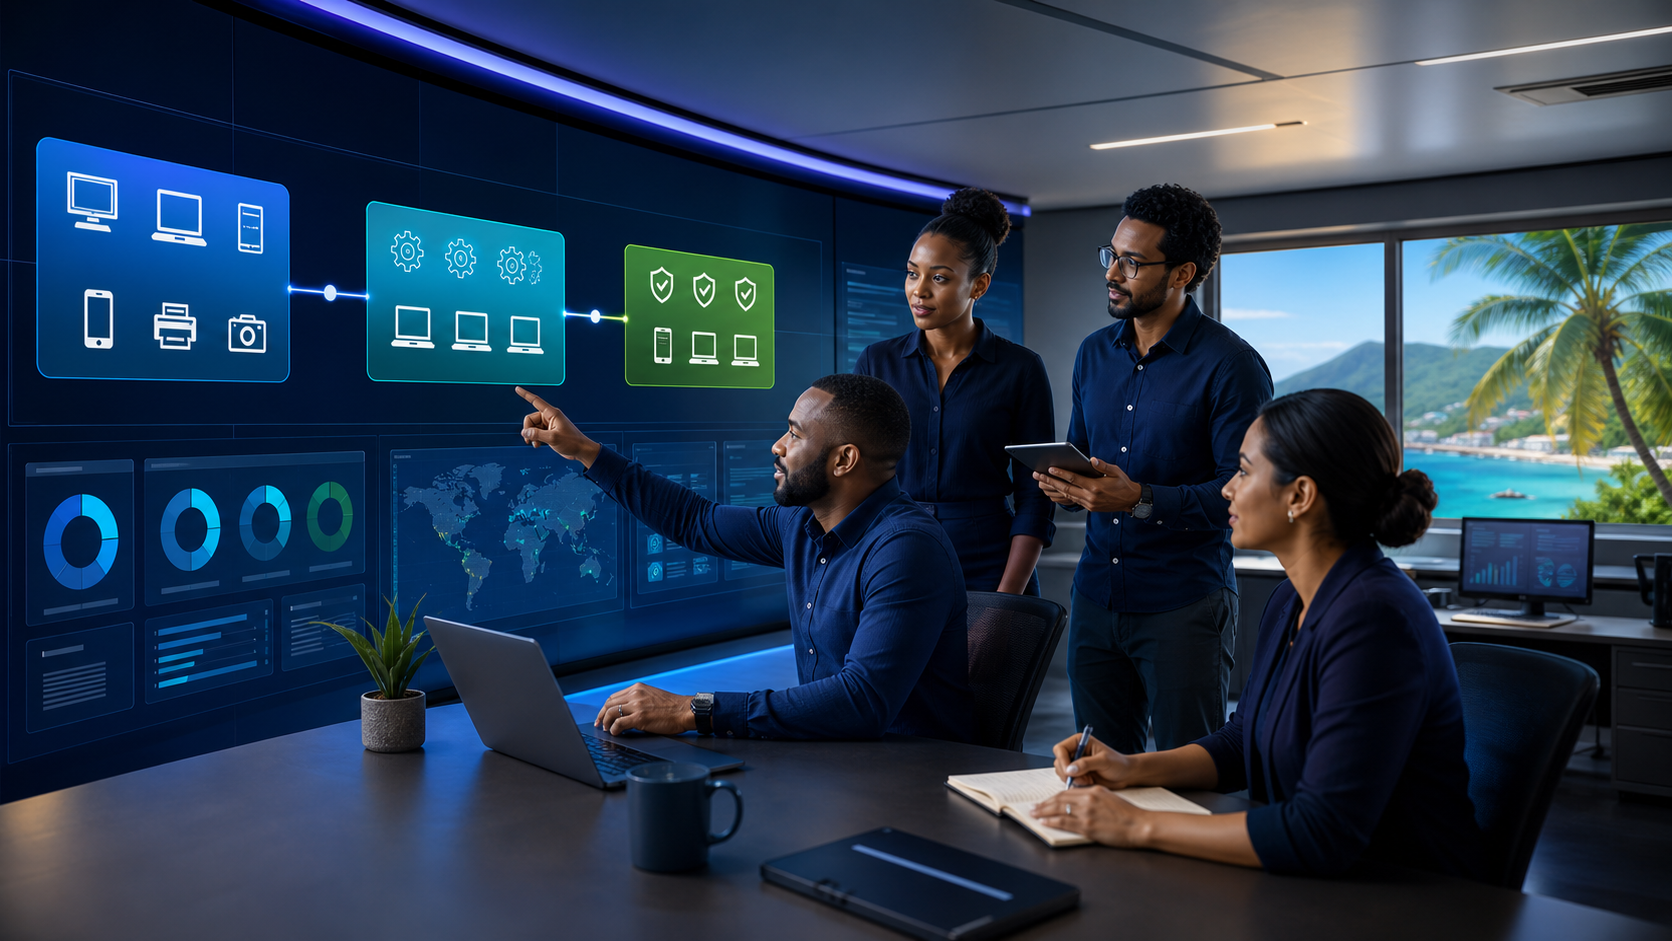
Patch management fails when nobody can answer three questions: what is installed, what is missing and who owns the fix. GFI LanGuard is positioned to help teams assess network devices, identify missing updates and manage remediation from one operational view.
A long vulnerability list is not a patch plan. When a flaw has credible evidence of exploitation, it should move ahead of issues that are severe only on paper. CISA maintains the Known Exploited Vulnerabilities Catalog to help defenders prioritise vulnerabilities being used in the wild.
Security software still needs lifecycle management. A gateway, mail-security platform or patch-management tool cannot protect the business well if the product itself is running an unsupported release.
Today is the second Tuesday of July, Microsoft’s normal security-update day. At 05:30 AST the July release details are not yet available, so responsible preparation means setting the workflow now and assessing the actual advisories when Microsoft publishes them.
A simple weekly routine for turning known-exploited-vulnerability guidance into practical cyber safety.
A practical weekly process for turning CISA known-exploited-vulnerability alerts into accountable business patching.
CISA added CVE-2026-45659 to its Known Exploited Vulnerabilities catalog on July 1, 2026. If your business runs on-premises SharePoint Server 2016, 2019, or Subscription Edition, this is a patch-now issue because attackers can turn low-level access into remote code execution.