Managed IT ServicesCybersecurity
Old Routers Are Becoming Attack Infrastructure
AryStinger shows why unsupported routers and forgotten NAS devices should be treated as business risk, not background hardware.
June 22, 2026
5 min read
Insights, tutorials, and news from our IT experts in Trinidad & Tobago.
AryStinger shows why unsupported routers and forgotten NAS devices should be treated as business risk, not background hardware.
Cyber Essentials offers a straightforward security baseline that Trinidad and Tobago SMBs can adopt without overcomplicating their operations. Here is how to turn those controls into managed, recurring practice.
CISA lists CVE-2026-42897 as known exploited. Businesses still running on-prem Exchange should verify mitigation, logs, and patch status now.
NAS Updates Should Be Managed Like Business Infrastructure Most small businesses understand that laptops and servers need updates. NAS and storage systems are...
Apex One Zero-Day Shows Why Security Tools Need Patch Management Too Security software is supposed to protect the business, but it still has to be treated like...
A newly disclosed Linux kernel ptrace flaw can expose sensitive files and lead to root-level execution. Businesses should confirm patch status, rebooted kernels, and credential rotation where risk is present.
CVE-2026-48172 is being exploited in the wild and can turn a compromised cPanel account into root-level server access. Here is what to check.
Two Microsoft Defender vulnerabilities are being exploited in the wild. Here is what business owners and IT teams should verify now.
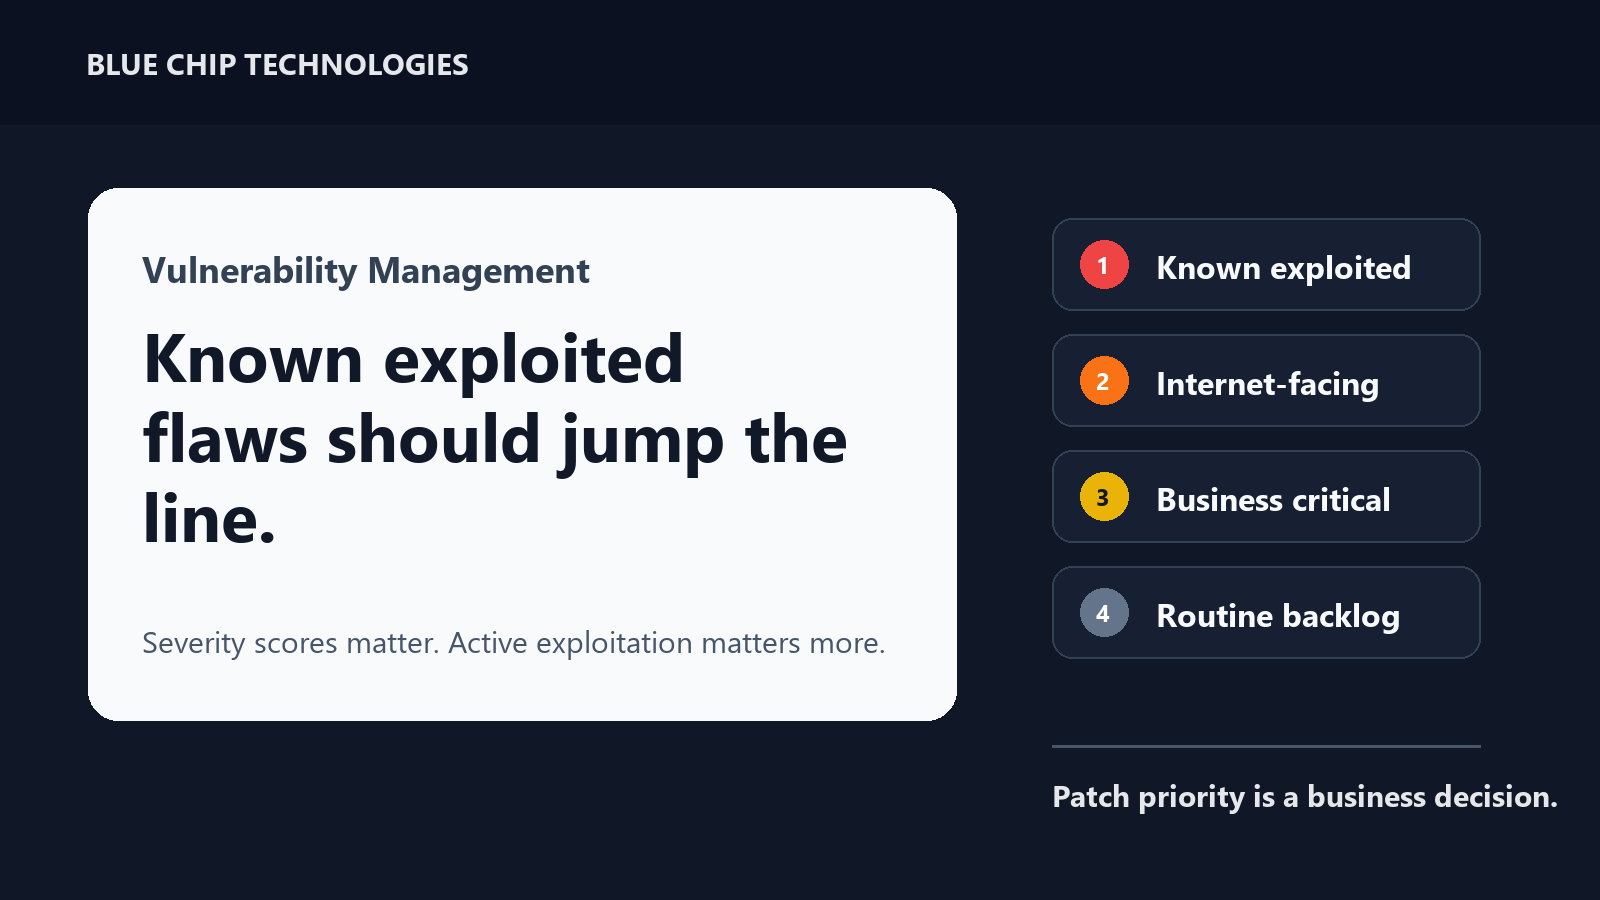
Known exploited vulnerabilities should not sit in the normal patch backlog. Give them a faster queue with ownership, deadlines, and proof.